Finance and Banking
On your own servers, with scoped permissions, approval chains and an audit trail
In financial institutions the first question about internal process software is security: will data leave the organisation, who can see what, and can every approval be traced afterwards? HibritİK answers with installation on the organisation’s own servers, permissions granted at own-record, team, department or organisation scope, and a change history kept inside each task.
Türk Eximbank uses the vehicle management module on its own servers: vehicle requests pass through an approval chain and fleet records are kept in one place. The same installation can also run project and task management, multi-step leave approval, the quality document library with its revision approval chain, CAPA and internal audit forms; the organisation decides which modules to enable.
References from this sector
 Türk EximbankOn the organization’s servers
This sector’s problems and the HibritİK answer
The problems organisations in this sector run into most often, and how HibritİK answers each one.
- 1Problem
Staff and process data leaving for an external cloud is not acceptable
With HibritİKHibritİK is installed on the organisation’s own servers; the on-premises edition is the same software as the cloud edition. Türk Eximbank works this way.
- 2Problem
Who can see which record is granted person by person and cannot be explained in an audit
With HibritİKPermissions are granted through roles, each limited to own-record, team, department or whole-organisation scope. Permissions of unlicensed modules have no effect, and a role change takes effect immediately.
- 3Problem
Approvals are given by e-mail, and who approved what and when cannot be found later
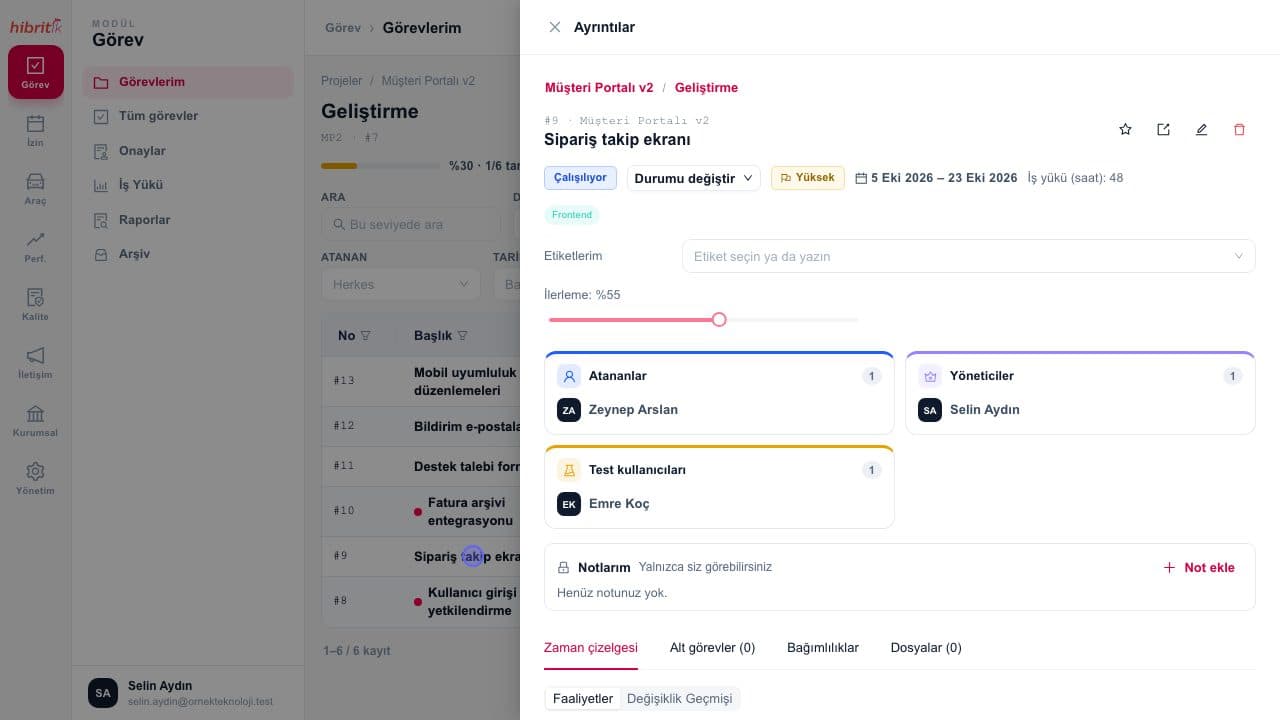
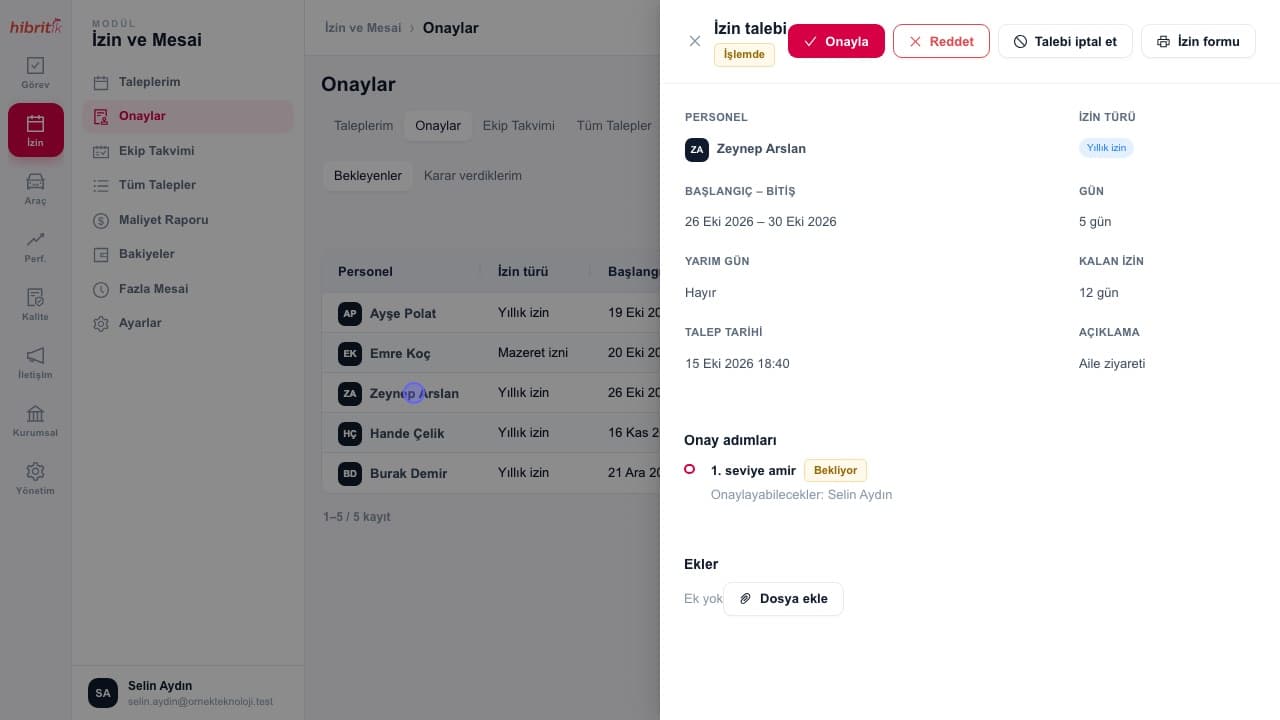
With HibritİKProject, leave, vehicle and document revision requests pass through multi-step approval chains; approval history and task changes are kept inside the record.
- 4Problem
Old versions of procedures and instructions stay in circulation
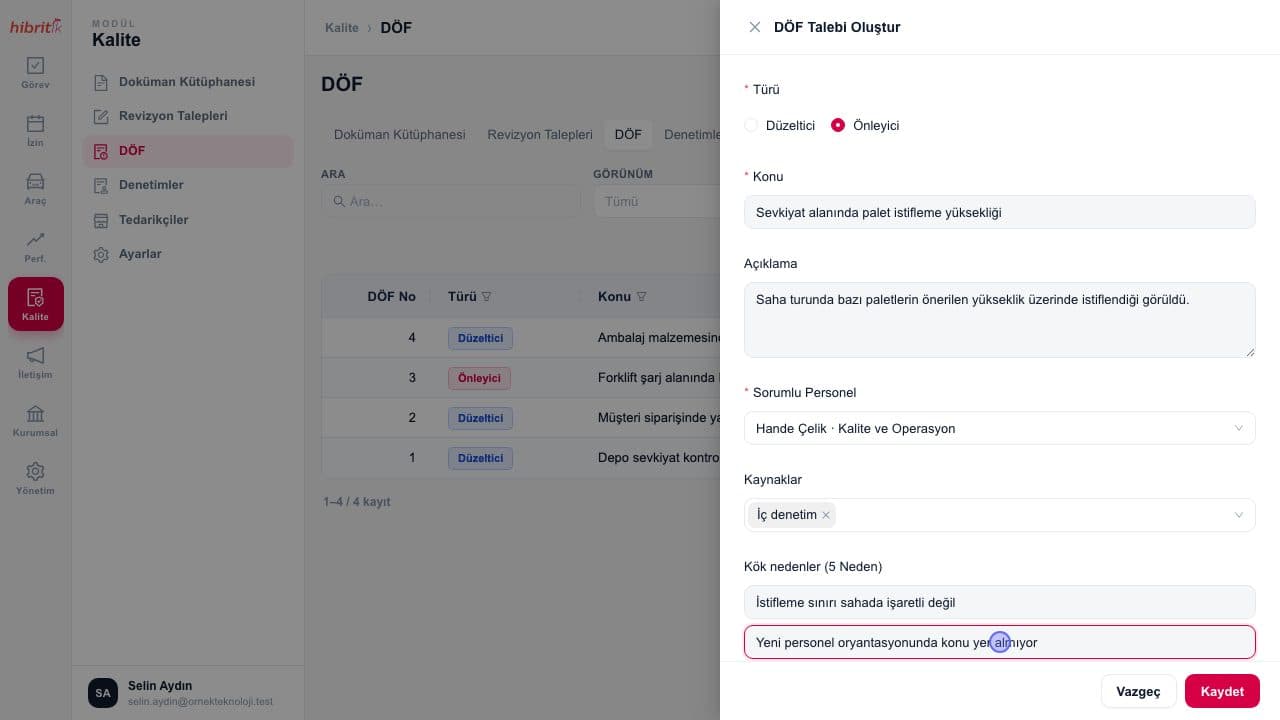
With HibritİKThe quality document library is kept with folders, revisions and distribution lists; employees confirm they have read the current version, and revisions pass through an approval chain configured per folder.
- 5Problem
A departed employee’s account stays open and active sessions are invisible
With HibritİKMembership is closed on the leaving date and open sessions drop; users can see and end their own sessions, login attempts are rate-limited and access tokens are short-lived.
Which modules stand out?
The modules work regardless of sector; these are the ones organisations in this sector benefit from most. Licensing is per module, so you enable only what you need.
Related features
Frequently asked questions
Can we start with a single module?
Yes. Licensing is per module; Türk Eximbank uses the vehicle management module. Modules that are not enabled stay hidden in the interface and their permissions have no effect.
Is there a summary for our security questionnaire?
Yes. The security and compliance page covers data location, encryption in transit and at rest, authorisation, backups, the KVKK process, ISO 27001 and sub-processors in a summary table.
How is integration with our existing systems done?
Through the REST API. Each integration gets its own account and an API key limited by role-based permissions; data exchange with existing HR and other systems is delivered as a project planned around your needs.
Other industries
Is your sector not on the list?
The modules work regardless of sector; try it free for 14 days with your own team, or tell us about your sector.